June 2026

IRDAI

IRDAI Dark Pattern Circular Explained | 15-Day Compliance Guide 2026

IRDAI Dark Pattern Circular Explained | 15-Day Compliance Guide Digital channels have transformed the insurance industry. From policy purchases and renewals to claims and customer support, almost every interaction now happens online. While this improves customer convenience, it also increases the risk of deceptive user interface (UI) and user experience (UX) practices, commonly known as dark patterns. Recognizing these risks, the Insurance Regulatory and Development Authority of India (IRDAI) has directed insurers to comply with the Guidelines on Prevention and Regulation of Dark Patterns issued by the Central Consumer Protection Authority (CCPA). The circular requires insurers to review their digital platforms and submit compliance within 15 days, making this a priority for every insurance company operating in India. Executive Summary The IRDAI circular requires insurers to eliminate deceptive digital practices across websites, mobile applications, customer portals, and digital journeys. Organizations must review their digital interfaces, identify potential dark patterns, implement corrective measures, and ensure compliance within the prescribed timeline. Ignoring the circular could lead to regulatory scrutiny, customer complaints, reputational damage, and legal consequences. What Are Dark Patterns? Dark patterns are user interface designs that intentionally influence or manipulate users into making decisions they may not have otherwise made. In the insurance industry, these practices undermine customer trust and violate fair digital guidelines. Hidden charges during checkout Pre-selected add-on covers Difficult cancellation processes Misleading countdown timers Forced marketing communications Confusing privacy configurations Disguised advertisement banners Hidden opt-out links Visualizing Deceptive UI vs. Transparent Compliance The core of the IRDAI guideline centers around choice. Below is a comparative illustration of how a common checkout transaction is rendered in a deceptive format versus a transparent, compliant format: ⚠ Deceptive (Dark Pattern) Pre-Selected Add-on Standard Health Cover Base Premium: ₹4,000 + Critical Illness Rider: ₹299 Accidental rider has been added automatically for your protection. (Difficult to deselect) Total Charges: ₹4,299 Proceed to Pay ✓ Transparent (Compliant) User-Driven Opt-in Standard Health Cover Base Premium: ₹4,000 Critical Illness Rider (Optional): ₹299 Yes, add Critical Illness Cover for ₹299/year. Total Charges: ₹4,000 Confirm & Pay The circular requires insurers to dismantle these pre-selected structures, hidden co-payments, and bundled choices, ensuring that customer consent is actively, freely, and transparently given. Side-by-Side Deceptive UX vs. Compliant UX Comparison Deceptive Pattern (❌ Action Required) Transparent Solution (✅ Standard Practice) ❌ Hidden Charges Adding unexpected service charges, processing costs, or extra fees during policy checkout. ✅ Upfront Pricing Clear, immediate display of the base premium and exact cost breakdowns. ❌ Pre-Selected Add-ons Auto-checking riders, accident covers, or co-payments before the customer selects them. ✅ Active Opt-in Empty checkmarks requiring direct, positive user clicks to add extra covers. ❌ Obstructed Cancellation Making policy cancellation or refunds unnecessarily complicated or difficult to access. ✅ Easy Opt-out Clear, accessible account options and simple procedures for cancellation. ❌ Misleading Urgency Using false countdown timers to prompt immediate purchase decisions. ✅ Fair Urgency Info Accurate disclosures of offer timelines and policy terms. Why the IRDAI Dark Pattern Circular Matters The insurance industry relies heavily on customer confidence. Policyholders expect transparency when purchasing insurance products and sharing sensitive personal information. Transparent customer journeys Fair consent mechanisms Honest financial disclosures Ethical digital design guidelines Consumer-first interface paths The regulatory environment in India is shifting rapidly toward consumer protection and digital safety. Alongside this circular, organizations must also prepare for broader national regulations like DPDP Act compliance which mandate rigorous data privacy controls and user consent safeguards. For insurance organizations, aligning digital UX design with these legal standards is no longer merely about avoiding penalties—it is about building sustainable digital trust. Hidden Risks Most Insurers Overlook Many organizations assume dark patterns are limited to aggressive marketing practices. In reality, they often appear unintentionally during website redesigns, mobile app development, or third-party integrations. This makes a comprehensive cybersecurity risk assessment critical for identifying design flaws, data flow vulnerabilities, and interface irregularities that expose the firm to compliance penalties. Furthermore, digital integrations with vendors are a common source of compliance drift. Insurance companies should conduct a structured third-party risk assessment to ensure that external plugins, payment gateways, and agent portals do not introduce deceptive patterns that could violate regulatory expectations. Policy Purchase Journey Auto-selected riders & covers Hidden premium costs Misleading discount structures Customer Portals Obstructed account deletion Hidden cancellation flows Complicated refund requests Mobile Applications Forced device permissions Misleading alert notifications Automatic promotional opt-ins Marketing & Alerts Pre-checked consent checkboxes Difficult unsubscribe routes Confusing promotional offers Business Impact Failure to comply can create significant business challenges. Regulatory Risk: IRDAI may seek explanations or require corrective actions for non-compliance. Navigating these overlapping mandates requires professional security compliance consulting to verify compliance postures, draft governance frameworks, and establish defensible audit logs. Customer Trust: Consumers increasingly expect transparent digital experiences. Poor practices may reduce customer confidence and loyalty. Legal Exposure: Dark patterns may attract consumer complaints under applicable consumer protection regulations. Brand Reputation: Negative publicity surrounding deceptive digital practices can damage brand credibility. What Should Insurers Do Within 15 Days? A practical compliance approach includes: 01 Review Digital Assets Assess website checkouts, customer-facing applications, agent onboarding platforms, and customer portals. Performing continuous API security testing ensures that backend data structures do not inadvertently force consent or leak sensitive customer credentials. 02 Assess UX & Data Triggers Review consent mechanisms, checkout flows, pricing displays, cancellation journeys, and privacy notices to isolate manipulative triggers or pre-checked opt-ins. 03 Rectify and Document Remove manipulative design and hidden charges. Maintain structured evidence of reviews conducted, changes implemented, governance approvals, and internal audits. Expert Observation At Lumiverse Solutions, we frequently notice that organizations focus heavily on cybersecurity and data privacy while overlooking UX practices that create regulatory exposure. Many dark patterns are introduced unintentionally through marketing optimization or third-party plugins rather than deliberate misconduct. Regular reviews help identify these issues before they become compliance concerns. Compliance Checklist ✓Website reviewed ✓Mobile app assessed ✓Customer journey validated ✓Consent mechanisms reviewed ✓Pricing transparency confirmed ✓Cancellation process simplified ✓Privacy notices updated ✓Marketing communications verified ✓Third-party integrations reviewed ✓Compliance evidence documented

IRDAI Dark Pattern Circular Explained | 15-Day Compliance Guide 2026 Read More »

api testing

API Security Testing Guide for Modern Businesses: Protecting Business Growth Beyond the Code

API Security Testing Guide for Modern Businesses: Protecting Business Growth Beyond the Code APIs Power Modern Businesses But They Also Create Hidden Cybersecurity Risks Every digital business today depends on APIs. Whether customers are logging into a mobile banking application, placing an order on an e-commerce platform, integrating with a payment gateway, accessing healthcare records, or using enterprise SaaS software, APIs silently handle thousands of transactions every second. They have become the invisible engine behind modern digital transformation. Yet, while organizations continue investing in application development, cloud infrastructure, and customer experience, APIs frequently remain one of the least understood and least protected components of the technology ecosystem. This creates a dangerous misconception. Many organizations believe that securing the application automatically secures the APIs behind it. In reality, attackers rarely think this way. Instead of attacking the application’s interface, they increasingly target the APIs responsible for processing business logic, exchanging sensitive information, and authorizing user actions. The result is often data exposure, unauthorized transactions, compliance violations, and significant reputational damage. For modern businesses, API Security Testing is no longer just another security assessment. It has become a critical business control that protects customer trust, supports regulatory compliance, and enables organizations to innovate without exposing unnecessary cyber risk. Executive Summary API Security Testing is the process of identifying vulnerabilities, validating exploitability, and assessing the resilience of Application Programming Interfaces (APIs) against real-world attack scenarios. Unlike traditional application testing, API security focuses on authentication, authorization, data exposure, business logic flaws, and API misuse that could compromise business operations. For organizations building customer-facing applications, partner integrations, or cloud-native platforms, continuous API Security Testing reduces security risks, strengthens compliance readiness, and protects long-term business resilience. Why API Security Has Become a Boardroom Discussion A few years ago, API security was largely viewed as a technical responsibility handled by development teams. Today, it has become a strategic business concern. Why? Because APIs now power: Customer portals Mobile applications Banking integrations Payment systems Healthcare platforms SaaS products Supply chain integrations IoT ecosystems Every API exposes business functionality. Every exposed function represents a potential attack surface. As organizations expand their digital ecosystems, they also expand opportunities for attackers. The challenge is that many API vulnerabilities remain invisible during conventional security testing. This means organizations may confidently deploy secure-looking applications while hidden API weaknesses continue operating behind the scenes. The Business Impact of Insecure APIs API security is often discussed as a technical issue. In reality, its consequences extend far beyond IT. Operational Impact Compromised APIs can interrupt critical business services, resulting in downtime, failed transactions, and disrupted customer experiences. For businesses operating around the clock, even a short disruption can affect productivity and revenue. Customer Trust Modern customers expect secure digital experiences. An API-related breach that exposes personal information or transaction data can significantly reduce customer confidence and negatively influence long-term brand reputation. Trust, once lost, is expensive to rebuild. Compliance Exposure Regulations such as ISO 27001, SOC 2, PCI DSS, DPDP Act, HIPAA, and GDPR expect organizations to implement appropriate controls for protecting sensitive information. Since APIs frequently process regulated data, inadequate API security can contribute to compliance findings and regulatory scrutiny. Financial Consequences API-related incidents often involve emergency remediation, legal expenses, customer notification, incident response costs, business disruption, and revenue loss. The financial impact usually exceeds the cost of proactive security testing. What Most Organizations Overlook About API Security One of the most common misconceptions is that APIs are simply another component of the application. They are not. APIs are direct gateways to business data and functionality. While web applications have traditionally received significant security attention, APIs increasingly expose: Customer information Payment processing Authentication services Inventory management Financial transactions Internal business operations Attackers understand this shift. Organizations often underestimate it. Expert Observation At Lumiverse Solutions, one recurring challenge we observe during security assessments is that organizations maintain strong perimeter security while overlooking the APIs connecting internal systems, cloud services, and third-party platforms. Many of these APIs remain undocumented, insufficiently tested, or inherited through legacy integrations. These hidden interfaces frequently become attractive targets because they receive less visibility than customer-facing applications. Why Traditional Security Testing Often Misses API Risks Many organizations continue relying primarily on: Infrastructure security Vulnerability scanners Web application testing Network assessments These remain essential. However, APIs introduce unique attack scenarios. For example, a vulnerability scanner may confirm that an endpoint exists. It may not determine whether: One customer can access another customer’s data Business rules can be manipulated Authorization controls can be bypassed Sensitive information is unnecessarily exposed Rate limits can be abused These weaknesses frequently require manual testing, contextual analysis, and attacker-focused thinking. Area Web Application Testing API Security Testing Primary Focus User interfaces (UI), forms, and client-side validation scripts. Programmatic endpoints, backend integration layers, and raw payloads. Main Vulnerability Target Cross-Site Scripting (XSS), SQL Injection in input fields, and CSRF. Broken Object Level Authorization (BOLA), logic flaws, and token abuse. Data Formats HTML pages, static assets, and form data. Structured JSON, XML payloads, and API parameters. Tool Compatibility Automated crawlers map directory structures and user forms. Requires OpenAPI/Swagger documentation specs to map endpoints. Logic Validation Simple user journeys (e.g., clicking buttons, submitting fields). Chained multi-step transactions manipulating parameters and workflows. Understanding the OWASP API Security Top 10 The OWASP API Security Top 10 has become one of the most respected references for identifying common API security weaknesses. Rather than viewing it as a technical checklist, organizations should consider it a business risk framework. Broken Object Level Authorization (BOLA) This remains one of the most common API vulnerabilities. It occurs when users can access objects or records belonging to other users simply by modifying identifiers. Business impact: Customer data exposure, privacy violations, regulatory penalties, and loss of trust. Broken Authentication Weak authentication controls allow attackers to impersonate legitimate users or gain unauthorized access. Common causes include weak token management, session weaknesses, and poor credential handling. Business impact: Unauthorized account access, fraudulent transactions, and compromised customer identities. Broken Function Level Authorization Users gain

API Security Testing Guide for Modern Businesses: Protecting Business Growth Beyond the Code Read More »

Why Automated Vulnerability Scans Are Not Enough: The Business Value of Manual Penetration Testing

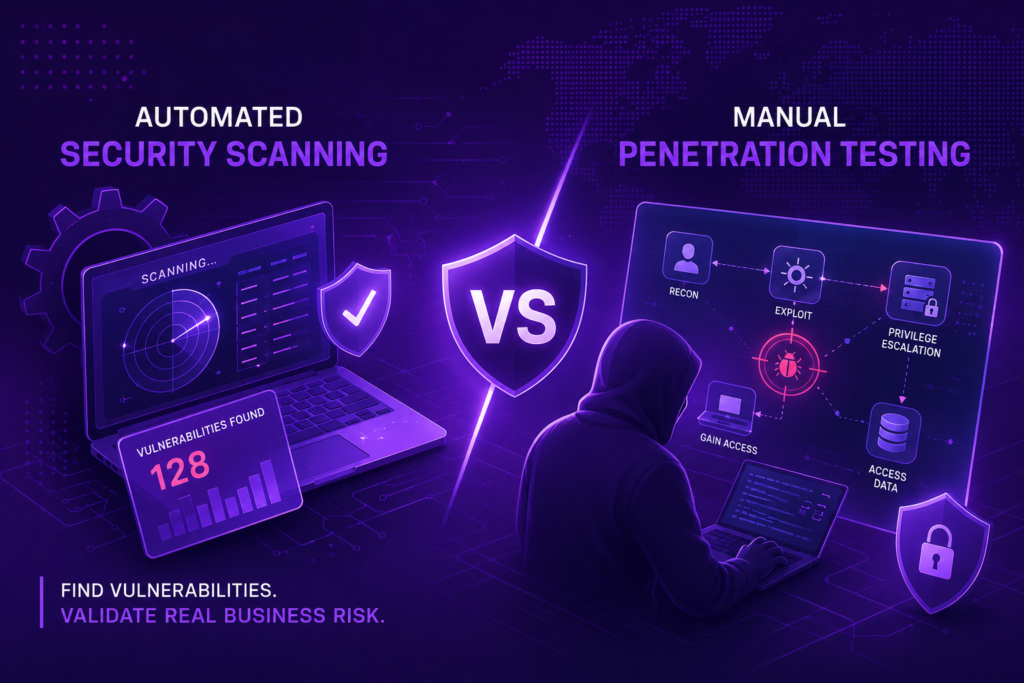
Why Automated Vulnerability Scans Are Not Enough: The Business Value of Manual Penetration Testing Your Security Dashboard Looks Green. So Why Do Organizations Still Experience Breaches? Many organizations invest in vulnerability scanners, endpoint security platforms, SIEM solutions, and automated security monitoring. Weekly reports show hundreds of vulnerabilities detected, dashboards indicate high compliance scores, and security teams receive automated alerts. Everything appears under control. Yet organizations with mature security programs continue to experience ransomware attacks, data breaches, API compromises, and unauthorized access incidents. The question leadership should ask is not: “Do we have security tools?” The better question is: “Do we truly understand how an attacker would exploit our environment?” That difference separates automated security scanning from manual penetration testing. While one identifies known weaknesses, the other validates how those weaknesses can become real business risks. Automated security scanning identifies known vulnerabilities across systems using predefined signatures and rules. Manual penetration testing goes further by simulating real-world attacks, validating exploitability, and uncovering business logic flaws, privilege escalation paths, and attack chains that automated tools frequently miss. Organizations seeking meaningful cybersecurity resilience should view these approaches as complementary rather than interchangeable. Why This Matters More Than Ever in 2026 Enterprise environments have changed dramatically. Applications communicate through APIs, cloud workloads scale dynamically, remote employees access critical systems from multiple locations, and third-party integrations expand attack surfaces daily. As infrastructure becomes more complex, attackers increasingly exploit combinations of seemingly low-risk vulnerabilities rather than a single critical flaw. Doing a comprehensive cybersecurity risk assessment is key. Unfortunately, automated scanners evaluate vulnerabilities individually. Attackers do not. The Biggest Misconception in Enterprise Cybersecurity One of the most common assumptions organizations make is: “If our vulnerability scanner doesn’t report critical findings, we must be secure.” This assumption creates dangerous blind spots. Automated tools are excellent at identifying known technical vulnerabilities. They are far less effective at understanding: Business workflows User behavior Authorization weaknesses Chained attack scenarios Logic manipulation Contextual risk At Lumiverse Solutions, one recurring finding during security assessments is that organizations often prioritize vulnerability counts instead of business impact. A report showing 300 low-risk vulnerabilities may receive immediate attention, while a single privilege escalation flaw capable of exposing sensitive customer data remains unnoticed. Security maturity is measured by understanding risk not simply counting vulnerabilities. Understanding Automated Security Scanning Automated security scanners systematically evaluate infrastructure, applications, endpoints, and networks for known weaknesses. They are valuable because they provide: Continuous visibility Fast vulnerability identification Large-scale coverage Compliance support Commonly identified issues include: Missing patches Weak configurations Outdated software Known CVEs SSL/TLS weaknesses Open ports For operational security, automated scanning is essential. But it has limitations. What Automated Security Scanning Cannot Tell You Automated tools rarely understand how applications actually function. They cannot reliably identify: Business Logic Abuse Example: An attacker bypasses payment verification without exploiting a technical vulnerability. Multi-Step Attack Chains Example: A low-risk misconfiguration linked with weak authentication, leading to privilege escalation, which ultimately exposes sensitive corporate data. Individually, each issue appears harmless. Combined, they become critical. Contextual Business Risk Automated tools may classify a vulnerability as “Medium.” However, for your specific business, that vulnerability may directly expose customer records, financial transactions, or intellectual property. Business context changes risk. Automation rarely understands that. Why Manual Penetration Testing Delivers Different Insights Manual penetration testing approaches systems the same way attackers do. Security professionals actively attempt to: Escalate privileges Abuse workflows Chain vulnerabilities Bypass authentication Exploit APIs Access restricted resources Instead of asking: “Does a vulnerability exist?” penetration testers ask: “Can this vulnerability actually compromise the business?” That shift changes everything. What Most Organizations Overlook Many organizations purchase vulnerability scanners believing they have replaced penetration testing. They haven’t. Scanning identifies weaknesses. Penetration testing validates risk. Those objectives are fundamentally different. Thought Leadership Perspective Security tools generate visibility. Experienced security professionals generate understanding. The strongest cybersecurity programs combine both. Automated Security Scanning vs Manual Penetration Testing Area Automated Scanning Manual Penetration Testing Speed Excellent Moderate Coverage Broad Targeted Known Vulnerabilities Excellent Excellent Business Logic Testing Limited Extensive API Abuse Testing Limited Strong Privilege Escalation Limited Strong Attack Chain Simulation No Yes Business Context Minimal High Risk Validation No Yes Strategic Recommendations Limited Comprehensive Why Compliance Alone Is Not Enough Organizations often conduct vulnerability scans because ISO 27001 requires risk management, SOC 2 expects testing, DPDP emphasizes security controls, or customer contracts require assessments. Compliance is important, but compliance does not always reveal exploitability. Passing an audit demonstrates control alignment; manual penetration testing demonstrates control effectiveness. There is a significant difference. Questions Leadership Should Ask Before relying solely on automated security reports, leadership should ask: Have critical findings been manually validated? Can vulnerabilities actually be exploited? Are APIs independently tested? Have business workflows been assessed? Can attackers move laterally across systems? Which risks create the greatest business impact? A Practical Enterprise Security Assessment Framework Assessment Area Key Question Asset Visibility Do we know what exists? Vulnerability Discovery Have known risks been identified? Exploit Validation Can weaknesses actually be exploited? Business Logic Review Can workflows be abused? API Security Are integrations secure? Privilege Management Can access be escalated? Remediation Are findings prioritized by business impact? Organizations that evaluate all seven areas generally achieve stronger security maturity than those relying on automated scanning alone. Enterprise Security Checklist Automated vulnerability scanning completed Manual penetration testing performed APIs independently assessed Authentication validated Authorization tested Business logic reviewed Cloud configurations verified Remediation prioritized Findings revalidated Expert Takeaways Organizations rarely experience breaches because they lacked security tools. They experience breaches because critical risks remained misunderstood. Automation provides scale, while human expertise provides context. Automation identifies weaknesses, while manual testing validates exposure. Neither replaces the other. The most resilient organizations integrate both into a continuous security program rather than treating security assessments as annual compliance exercises. Conclusion Automated security scanning remains an essential component of modern cybersecurity. But visibility alone does not reduce risk. Understanding how attackers think, how vulnerabilities interact, and how business processes can be abused requires human expertise. Organizations that combine automated scanning with

Why Automated Vulnerability Scans Are Not Enough: The Business Value of Manual Penetration Testing Read More »

Security Gaps

Why Most Organizations Discover Security Gaps Too Late: A Practical Cybersecurity Risk Assessment

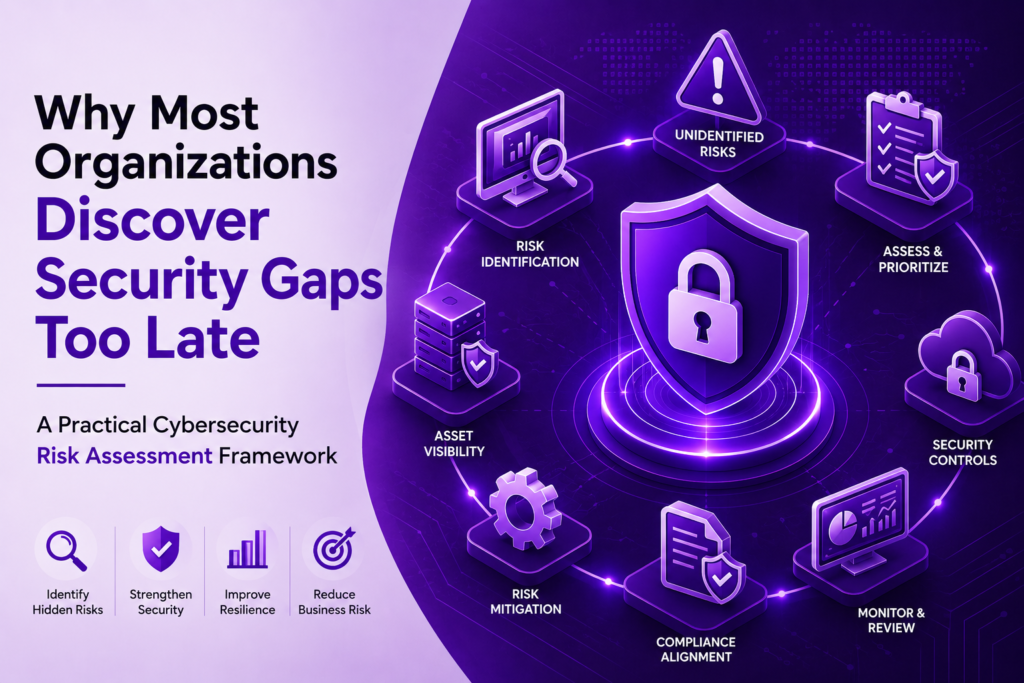
Why Most Organizations Discover Security Gaps Too Late: A Practical Cybersecurity Risk Assessment The Most Expensive Security Risks Are Often the Ones Nobody Knows Exist Most organizations don’t ignore cybersecurity. They invest in firewalls. Deploy endpoint protection. Conduct compliance reviews. Implement security policies. Yet breaches, ransomware incidents, compliance failures, and operational disruptions continue to occur. Why? Because many organizations focus on known risks while remaining unaware of hidden ones. In cybersecurity, the most dangerous vulnerabilities are rarely the ones already documented. The greatest risk often comes from security gaps that remain invisible until a security incident, compliance audit, customer complaint, or business disruption exposes them. By then, the cost of remediation is significantly higher. This is why cybersecurity risk assessments have evolved from a compliance exercise into a strategic business necessity. The objective is no longer simply identifying vulnerabilities. The objective is understanding where business risk exists before attackers, regulators, or customers discover it first. A Cybersecurity Risk Assessment helps organizations identify, evaluate, and prioritize security risks that could impact operations, customer trust, compliance obligations, and business continuity. Rather than focusing solely on technical vulnerabilities, a mature risk assessment evaluates how security weaknesses translate into real-world business exposure. Why Cybersecurity Risk Assessments Matter More in 2026 The modern enterprise environment is significantly more complex than it was even a few years ago. Organizations now operate across: Cloud platforms Hybrid infrastructure SaaS applications Remote work environments Third-party vendors APIs and integrations Every new digital initiative creates opportunity. It also creates risk. The challenge is that cybersecurity environments evolve much faster than traditional risk management processes. A control that was effective last year may no longer provide sufficient protection today. One of the biggest misconceptions in cybersecurity is assuming risk remains static. In reality, cyber risk is constantly changing because technology, threat actors, business processes, and attack surfaces continuously evolve. Organizations that assess risk once a year often underestimate how much their environment changes between assessments. Why Organizations Often Discover Security Gaps Too Late Most security incidents are not caused by a complete absence of security controls. They occur because organizations fail to recognize how risks accumulate across systems, people, processes, and technologies. At Lumiverse Solutions, one recurring challenge we observe during assessments is that organizations often have security tools in place but lack visibility into how those tools, systems, and processes interact. This creates hidden exposure that is difficult to detect without a structured risk assessment. What Most Organizations Overlook When leaders think about cybersecurity risk, they often focus on obvious threats: Malware Ransomware Data breaches While important, these are often symptoms rather than root causes. The underlying risks frequently include: Incomplete Asset Visibility Unknown assets cannot be protected. Excessive User Access Too many privileges create unnecessary exposure. Third-Party Dependencies Vendor weaknesses often become organizational risks. Unpatched Systems Known vulnerabilities remain exploitable. Misconfigured Cloud Environments Small configuration errors can create significant exposure. These issues rarely make headlines until something goes wrong. The Hidden Cost of Delayed Risk Discovery Many organizations evaluate cybersecurity primarily from a technical perspective. However, security gaps create broader business consequences. Operational Impact Security incidents disrupt business operations. Examples include: Application outages Service interruptions Productivity losses Compliance Impact Undiscovered risks can lead to: Audit findings Regulatory scrutiny Compliance violations Particularly under frameworks such as: ISO 27001 DPDP SOC 2 PCI DSS HIPAA Customer Trust Impact Trust is difficult to build and easy to lose. A single security incident can affect: Customer retention Vendor confidence Brand reputation Financial Impact Delayed risk identification often results in: Emergency remediation costs Legal expenses Operational recovery expenses Revenue loss The longer risks remain undiscovered, the more expensive they typically become. Common Misconceptions About Cybersecurity Risk Assessments Misconception #1 “We Passed Compliance, So We Must Be Secure” Compliance helps establish controls. It does not guarantee resilience against real-world threats. Misconception #2 “Our Security Tools Will Alert Us” Security tools generate visibility. They do not automatically eliminate risk. Misconception #3 “We Conduct Vulnerability Scans” Risk assessments evaluate broader business exposure beyond technical vulnerabilities. Misconception #4 “Nothing Has Happened Yet” Many organizations mistake the absence of incidents for the absence of risk. Those are not the same thing. Why Traditional Security Approaches Often Fail Traditional security programs often focus on individual controls. Risk assessments focus on the bigger picture. Thought Leadership Insight Cybersecurity failures rarely result from a single vulnerability. They typically occur when multiple weaknesses align. For example: Weak access controls Unpatched systems Poor monitoring Third-party exposure Individually, each issue may seem manageable. Collectively, they create significant business risk. A Practical Cybersecurity Risk Assessment Framework Organizations can use the following framework to evaluate security maturity. Risk Area Key Question Asset Visibility Do we know what needs protection? Identity & Access Who can access critical systems? Vulnerability Management Are risks remediated effectively? Cloud Security Are configurations secure? Third-Party Risk Are vendors assessed? Monitoring & Detection Can threats be identified quickly? Incident Response Can we respond effectively? Compliance Alignment Are controls aligned with obligations? This framework helps organizations move beyond compliance and toward resilience. Questions Leadership Should Ask Before assuming security maturity, leadership should ask: Do we know our highest-risk assets? Which risks pose the greatest business impact? Are we assessing third-party security exposure? How quickly can we detect security incidents? Have critical controls been tested recently? Are security investments reducing measurable risk? The answers often reveal more than security dashboards. Cybersecurity Risk Assessment Checklist Organizations should regularly evaluate: Asset inventory accuracy Access control effectiveness Vulnerability management processes Cloud security posture Vendor risk exposure Security monitoring capabilities Incident response readiness Compliance obligations Backup and recovery processes Security testing effectiveness Why Mature Organizations Treat Risk Assessments Differently Less mature organizations often perform assessments because regulations require them. More mature organizations perform assessments because leadership understands that visibility reduces uncertainty. Expert Insight The strongest cybersecurity programs are not necessarily the ones with the most tools. They are the ones with the clearest understanding of where risk exists and how it affects business priorities. That clarity often begins with

Why Most Organizations Discover Security Gaps Too Late: A Practical Cybersecurity Risk Assessment Read More »

Why Cybersecurity Audits Fail: Hidden Security Gaps Most Organizations Discover Too Late

Why Cybersecurity Audits Fail: Hidden Security Gaps Most Organizations Discover Too Late Few business events create more anxiety for leadership teams than an upcoming cybersecurity audit. Weeks are spent gathering documentation. Teams rush to close findings. Policies are updated. Reports are reviewed. Security controls are re-evaluated. Yet despite these efforts, organizations continue to encounter the same uncomfortable reality: Audit findings reveal security gaps that should have been identified long before the audit began. Even more concerning, many organizations successfully pass compliance reviews and still experience security incidents months later. This raises an important question: If organizations are investing heavily in compliance and audits, why do critical security gaps continue to exist? The answer is surprisingly simple. Many organizations prepare for audits. Very few prepare for actual security resilience. That difference often determines whether an audit becomes a confidence-building exercise or an expensive wake-up call. Cybersecurity audits often fail not because organizations lack security controls, but because they focus heavily on documentation, compliance checklists, and point-in-time reviews while overlooking deeper operational, technical, and governance weaknesses. The most successful organizations treat audits as a validation process not their primary security strategy. Why Cybersecurity Audits Matter More Than Ever Today’s organizations operate in increasingly complex digital environments. Hybrid infrastructure Cloud applications Remote workforces Third-party vendors APIs and integrations Expanding attack surfaces At the same time, regulatory expectations continue to increase across industries. Organizations are expected to demonstrate security readiness through frameworks and regulations such as: ISO 27001 SOC 2 PCI DSS DPDP HIPAA RBI Security Guidelines The challenge is that modern threats evolve continuously. Audits typically evaluate a specific point in time. Attackers do not. This creates a dangerous gap between compliance status and actual security posture. Leadership Perspective Organizations that view cybersecurity audits solely as compliance requirements often miss the broader objective: strengthening operational resilience against evolving threats. An audit should confirm security maturity—not create it. The Biggest Misconception About Cybersecurity Audits One of the most common assumptions organizations make is: “If we pass the audit, we must be secure.” Unfortunately, cybersecurity does not work that way. An audit validates specific controls against a defined framework. Security is significantly broader. A compliance review may verify that policies exist, evidence is documented, and required controls are implemented. However, attackers do not target documentation. Attackers target weaknesses. This distinction is often overlooked during audit preparation. Thought Leadership Insight Passing an audit demonstrates that controls exist. It does not always demonstrate that those controls remain effective under real-world attack conditions. Security requires continuous validation, testing, monitoring, and improvement beyond compliance requirements. What Most Organizations Overlook Many security programs become heavily focused on audit preparation activities such as: Policy documentation Control mapping Evidence collection Compliance reporting Framework alignment Audit artifact preparation While these activities are important, they can create a false sense of confidence when not supported by ongoing security validation. Organizations often know which controls should exist. The challenge is determining whether those controls are actually functioning effectively during day-to-day operations. This gap frequently becomes visible during audits and assessments. Hidden Security Gaps That Cause Audit Failures Most audit findings stem from a handful of recurring weaknesses that remain hidden until formal reviews expose them. Gap #1: Asset Visibility Problems You cannot secure what you cannot see. Many organizations struggle to maintain complete visibility across rapidly evolving environments. Common examples include: Cloud assets Shadow IT systems Legacy infrastructure Development environments Temporary project resources Third-party integrations When assets remain undiscovered, they frequently become unmanaged. Unmanaged assets often become attack surfaces. Business Impact Asset visibility gaps can lead to compliance failures, vulnerability exposure, security blind spots, and increased attack opportunities. Gap #2: Access Control Weaknesses Access management remains one of the most common findings across cybersecurity audits and compliance assessments. As organizations grow, user access rights often accumulate over time. Employees change roles, contractors gain temporary access, and privileged accounts are created to support operational requirements. Without proper governance, these permissions can quickly become excessive. Common access control weaknesses include: Excessive user permissions Dormant user accounts Privileged access misuse Shared administrative credentials Incomplete access reviews Weak role-based access controls Business Impact Poor access governance increases the risk of unauthorized access, insider threats, data exposure, and regulatory violations. Many organizations discover these issues only during audits, despite the fact that they often exist for months or years beforehand. Gap #3: Vulnerability Management Gaps Most organizations conduct vulnerability scans. Far fewer organizations consistently remediate the vulnerabilities they discover. Cybersecurity audits frequently identify weaknesses in vulnerability management programs rather than a lack of scanning activity. Common challenges include: Delayed patch deployment Unclear remediation ownership Limited resource availability Poor risk prioritization Inconsistent vulnerability tracking Lack of executive visibility Organizations often assume that discovering vulnerabilities is enough. In reality, risk reduction only occurs when vulnerabilities are effectively remediated. Practical Reality A vulnerability identified but not remediated remains a vulnerability. Threat actors are not concerned with whether a weakness appears on a report. They only care whether it remains exploitable. Gap #4: Third-Party Risk Blind Spots Modern organizations rely heavily on external vendors, cloud providers, consultants, software platforms, and service providers. These third parties often process sensitive information, connect directly to business systems, or support critical business operations. Despite this reliance, vendor security reviews are frequently limited or performed only during onboarding. Common third-party risk gaps include: Insufficient vendor assessments Lack of continuous monitoring Incomplete contractual security requirements Poor visibility into vendor security practices Weak supply chain security governance Business Impact Third-party weaknesses can introduce compliance challenges, operational disruption, data exposure, and supply chain risks that directly affect the organization. As regulatory expectations increase, organizations are increasingly accountable for managing third-party security risks. Gap #5: Security Controls Exist but Are Not Tested One of the most overlooked causes of audit findings is the assumption that implemented controls automatically remain effective. Organizations frequently deploy security controls and then rarely validate them afterward. Examples include: Backup systems Incident response plans Security monitoring controls Disaster recovery procedures Access management workflows Business continuity plans Documentation may

Why Cybersecurity Audits Fail: Hidden Security Gaps Most Organizations Discover Too Late Read More »

Web Application Penetration Testing (WAPT)

Web Application Penetration Testing (WAPT) Most Application Breaches Start Quietly A lot of companies think their web applications are safe just because they use HTTPS, set up firewalls, and periodically run vulnerability scans. But breaches still happen again and again. What’s unsettling is that application security problems often linger for months, sometimes years, before anyone notices. Most of the time these are not advanced exploits. They are basic weaknesses in authentication, session management, APIs, access controls, and business workflows. These small gaps quietly create opportunities for attackers. By the time they are discovered, customer trust has already been affected, compliance obligations become more difficult, and operational disruption increases. That is why Web Application Penetration Testing (WAPT) matters. It is not simply about identifying vulnerabilities. It is about understanding how attackers could exploit your applications before they do. Quick Summary Web Application Penetration Testing (WAPT) is a hands-on security assessment where experts simulate real-world attacks against web applications. The goal is to uncover vulnerabilities, validate exploitability, and identify security risks that automated tools often miss. If your organization handles customer information, digital transactions, APIs, SaaS platforms, or business-critical applications, WAPT helps identify weaknesses before they become costly business problems. Why Web Application Security Has Become Critical Applications are now the primary way organizations interact with customers. Customer portals SaaS platforms Mobile application backends E-commerce systems Internal business applications These applications often contain sensitive data and critical business functionality. As a result, they have become high-value targets for attackers. Traditional security controls typically focus on infrastructure. Attackers focus on applications. That gap creates risk. What Companies Often Miss A common misconception is: “If our infrastructure is secure, our application is secure.” In reality, application security is a completely different challenge. You can have a well-protected server while still hosting a vulnerable application. An application can pass compliance requirements and still contain exploitable business logic flaws. A vulnerability scanner can produce a clean report while critical risks remain hidden. These are the issues penetration testing is designed to uncover. Why Standard Security Testing Is Not Enough Many organizations rely heavily on: Automated vulnerability scans Compliance checklists Security tool outputs While useful, these approaches have limitations. Automated tools are effective at identifying known vulnerabilities but often struggle to detect: Business logic flaws Privilege escalation paths Multi-step attack chains Authentication weaknesses Authorization bypasses Real-world breaches frequently occur because attackers exploit workflows rather than technical vulnerabilities alone. Hidden Risks You Never See Coming Broken Access Control Broken Access Control remains one of the most common findings during Web Application Penetration Testing engagements. Users gain access to information, records, functions, or administrative features they should never be able to access. This often leads to: Unauthorized data exposure Privacy violations Regulatory penalties Loss of customer trust Business Impact A single authorization flaw can expose thousands of customer records and create significant compliance challenges. Authentication Weaknesses Weak authentication controls continue to be a major attack vector. Examples include: Weak password policies Session management flaws Missing account lockout controls Multi-factor authentication gaps Credential reuse vulnerabilities Attackers frequently exploit these weaknesses to compromise user accounts and gain unauthorized access. Business Impact Compromised accounts often become the starting point for larger breaches. Business Logic Vulnerabilities Business logic vulnerabilities are among the most overlooked risks in modern applications. Unlike technical vulnerabilities, these weaknesses arise from flaws in how workflows are designed. Examples include: Manipulating discount systems Bypassing approval processes Unauthorized transactions Workflow abuse Subscription manipulation Traditional security scanners rarely identify these issues. Business Impact Organizations can suffer direct financial losses and operational disruption. API Security Gaps Modern applications increasingly rely on APIs. Unfortunately, APIs frequently expose sensitive functionality and data. Common API security weaknesses include: Broken authentication Broken object level authorization Excessive data exposure Rate limiting failures Improper access controls Poorly secured APIs are responsible for many modern data breaches. Business Impact Weak API security can expose customer records, financial information, business data, and sensitive transactions. Why Passing Compliance Does Not Mean You Are Secure Organizations frequently ask: “We passed ISO 27001, SOC 2, or PCI DSS. Are we secure?” The answer is not always. Compliance frameworks provide governance and security guidance. However, compliance is not the same as security validation. Frameworks may verify that controls exist. Penetration testing verifies whether those controls can withstand real-world attacks. The most mature organizations treat compliance as a baseline rather than a destination. What Leaders Should Ask Before Choosing a WAPT Provider Selecting a penetration testing provider should involve more than comparing pricing. Leadership teams should evaluate the following: Evaluation Area Questions to Ask Testing Methodology Does the provider perform manual testing or only automated scans? Business Logic Testing Will workflows and business processes be evaluated? API Security Are APIs included within the testing scope? Remediation Support Will the provider assist with vulnerability remediation? Risk Prioritization Will findings be prioritized based on business impact? Industry Knowledge Does the provider understand your regulatory environment? How to Evaluate Your Application Security Use the following framework to assess application security maturity. Area Assessment Question Authentication Can unauthorized users gain access? Authorization Can users access restricted functionality? Data Protection Is sensitive information protected? API Security Are APIs securely configured? Business Logic Can workflows be manipulated? Monitoring Can suspicious activity be detected? Remediation Is there a structured process for fixing issues? The more negative answers you have, the higher your potential exposure. Web Application Security Checklist Authentication mechanisms reviewed Access controls validated API security assessed Business logic reviewed Session management tested Sensitive data exposure evaluated Security monitoring enabled Independent penetration testing completed Expert Takeaways The most damaging application breaches rarely result from a single vulnerability. They occur when multiple weaknesses combine. Organizations often focus heavily on technical controls while overlooking: User behavior Business workflows Authorization weaknesses Process abuse opportunities Application logic flaws Web Application Penetration Testing bridges these gaps. The goal is not simply finding vulnerabilities. The goal is understanding how vulnerabilities impact business operations, customer trust, compliance obligations, and resilience. Understanding application risks before they become incidents helps improve

Web Application Penetration Testing (WAPT) Read More »